



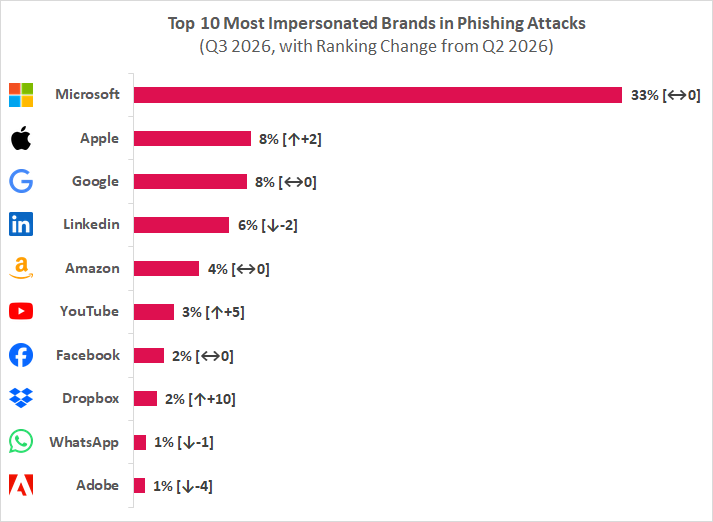
India– Check Point Research (CPR), the Threat Intelligence arm of Check Point® Software Technologies Ltd., a pioneer and global leader of cyber security solutions, today released its Brand Phishing Ranking for Q3 2026. The latest findings reveal that Microsoft remained the most impersonated brand, accounting for 33% of all brand phishing attempts tracked during the quarter, up from 23% in Q2. Attackers continue to exploit trust in widely used technology, social networking and financial brands, while also following users into AI and developer tools.
The concentration at the top of the ranking remained pronounced. Apple rose two places to rank second at 8%, tied with Google in third, while LinkedIn fell two places to fourth with 6% and Amazon completed the top five at 4%. Together, these five brands accounted for more than half of all brand impersonation attempts, while Microsoft’s 33% share was roughly four times that of any other brand.
Beyond the ranking, Q3 also brought a shift in tactics. Attackers impersonated AI and developer platforms such as Claude and Google Antigravity, using fake billing alerts and malicious installation commands. Other campaigns moved beyond credential theft by persuading victims to run terminal commands or install legitimate remote access software themselves.
This evolution is also reflected at industry level. Technology remained the most impersonated sector, followed by Social Networks and Banking—areas where people keep some of their most valuable accounts, from work email and cloud storage to social profiles and financial information.
Omer Dembinsky, Data Research Manager at Check Point Research, said, “Brand phishing is entering a new phase. Attackers are still exploiting trust in the technology platforms people use every day, but they are also following users into AI and developer tools and moving beyond password theft to convince victims to run malicious commands or install remote access software themselves. As generative AI makes convincing emails and cloned websites easier to produce at scale, organisations need prevention that reaches both the inbox and the wider web.”

Real-World Phishing Campaigns Observed in Q3 2026
The campaigns observed during the quarter illustrate how these tactics are being applied in practice, ranging from fake AI billing alerts and cloned support pages to malicious terminal commands and remote access software disguised as a required update.
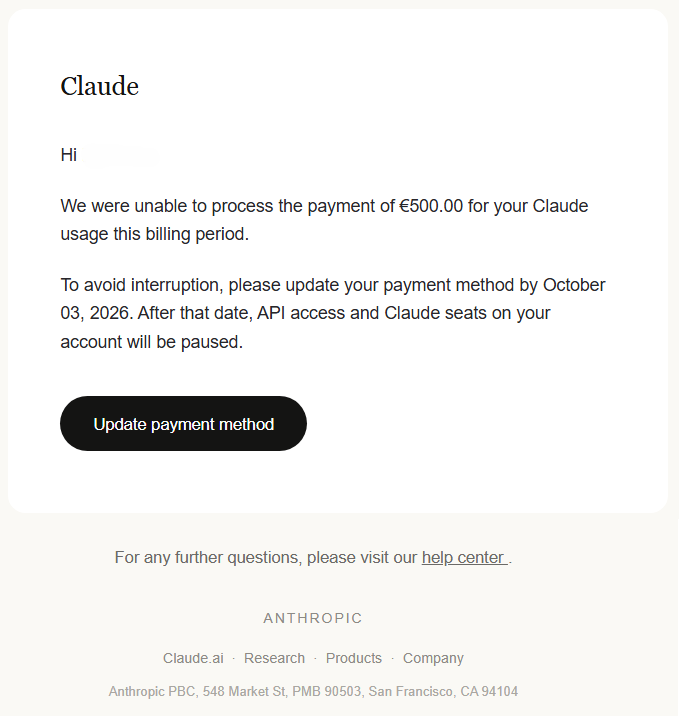
One campaign impersonated Claude through a fake payment failure email claiming that a €500.00 charge had been declined. The message warned that API access and Claude seats would be paused unless the recipient updated their payment method, placing both financial details and account credentials at risk.
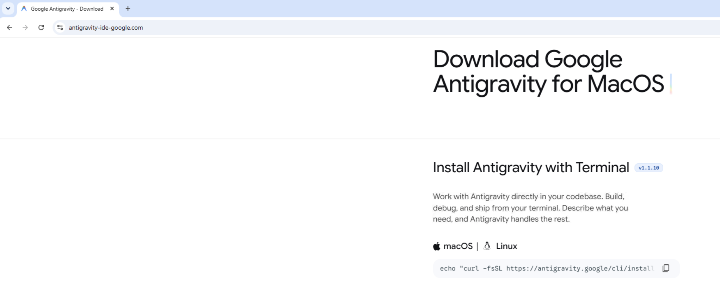
Another campaign used a lookalike Google Antigravity website that displayed what appeared to be a legitimate Linux installation command. In reality, the command decoded and ran a Base64-encoded instruction that downloaded and executed a shell script from an external server, giving the attacker remote code execution on the victim’s system.
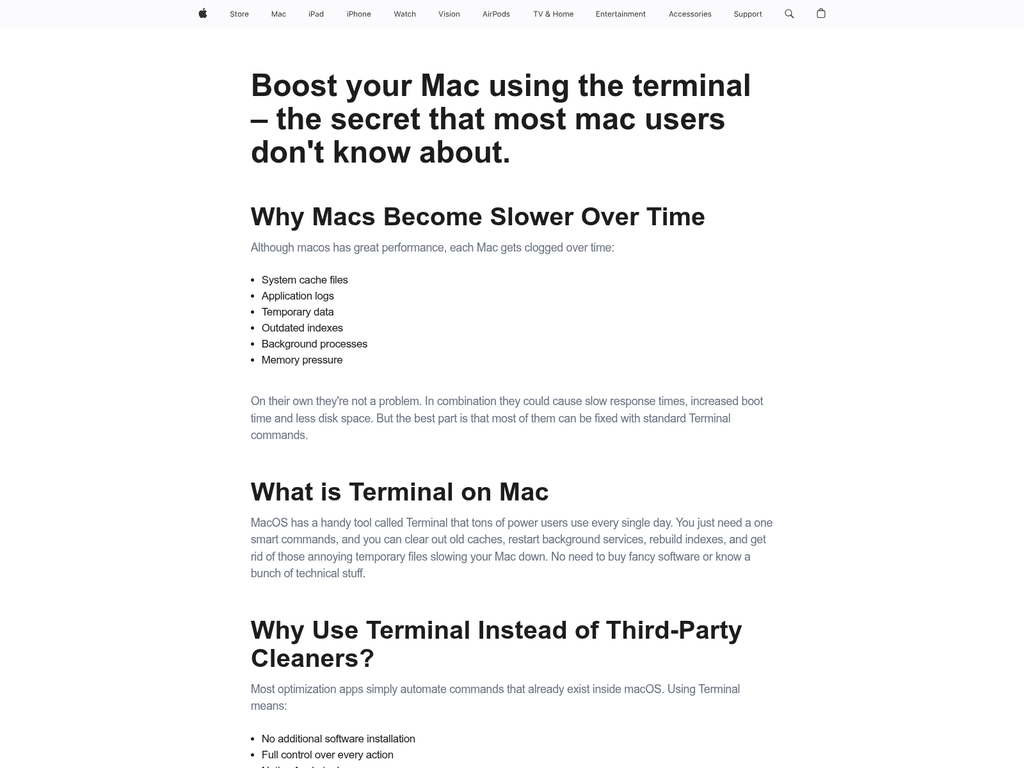
Attackers also created a fake Apple support article that encouraged Mac users to run terminal commands under the promise of improved performance. In a separate case, a spoofed Docusign site presented a document for review and claimed that a reader update was required; clicking Continue downloaded FleetDeck, a legitimate remote monitoring and management tool that could be abused to gain unauthorised access to the victim’s device.
Taken together, these cases show why brand phishing is becoming harder to contain. The attacks exploit trust in familiar names rather than a flaw in software, combining urgency, convincing branding, lookalike domains and apparently legitimate installation steps to lower suspicion. They also show how the objective is expanding beyond harvesting passwords and payment details to gaining direct control of devices.
As generative AI helps attackers produce convincing emails and fake websites at scale, prevention becomes more valuable than cleanup. Organisations should stop phishing messages before they reach inboxes, use AI-powered detection for brand impersonation and credential harvesting, automate investigation and response, monitor for unapproved remote management tools, and scan the wider web for lookalike domains and cloned login pages so fraudulent sites can be removed before customers engage with them.